What Open-AudIT can do
Open-AudIT tells you exactly what is on your network, how it is configured and when it changes, without agents. The Free edition covers up to 100 devices. Features marked Professional or Enterprise need a commercial edition.
Agentless Discovery.
Automatically detect every device on your network (servers, switches, printers, VMs) without installing agents.
Open-AudIT scans your subnets and identifies each device from what its open ports reveal, with no credentials needed for most of them. Large ranges are split into subnets and scanned in parallel. ARP tables, SSDP, NAS devices, service processors and OT devices over BACnet, Modbus, S7 and EtherNet/IP are all read, and version 7 knows 353 device types, up from 98. Credentialed audits over SNMP, SSH and WMI then collect the detail from servers, workstations, switches, routers, printers, phones and virtual machines.
Configuration Tracking.
Capture hardware and software configurations and alert when anything changes unexpectedly.
Every audit is stored, so you get a full timeline for each device. When a disk is swapped, software is installed or a setting changes, Open-AudIT records what changed and when.
Continuous Monitoring. (Professional) (commercial edition)
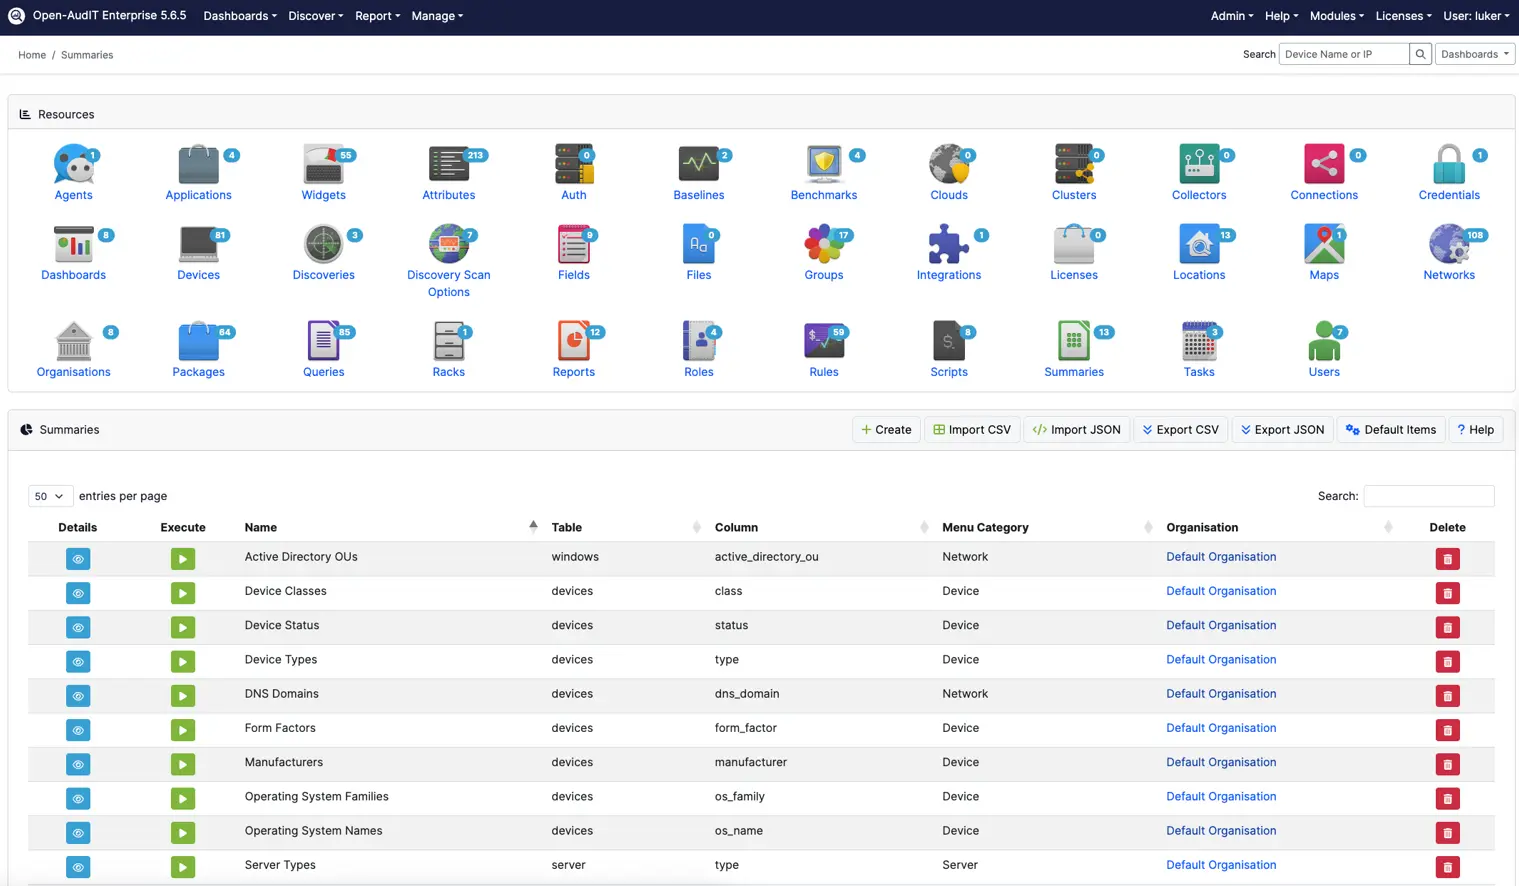
Schedule discoveries to run automatically so your asset inventory is always current.
Schedule discoveries hourly, daily or weekly. Your inventory stays current without anyone remembering to run a scan, and reports always reflect the network as it is today.
Vulnerability Detection. (Professional) (commercial edition)
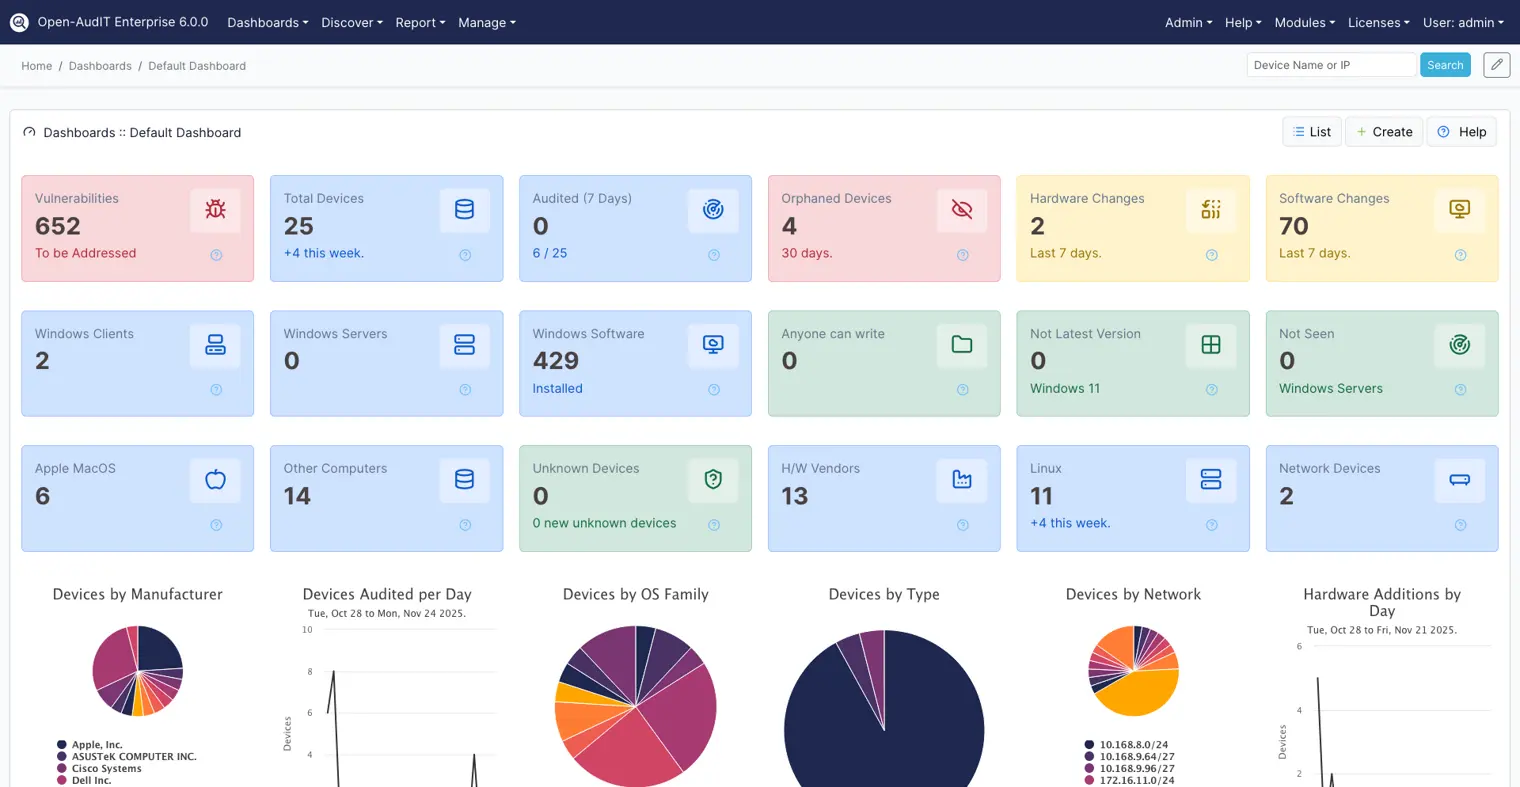
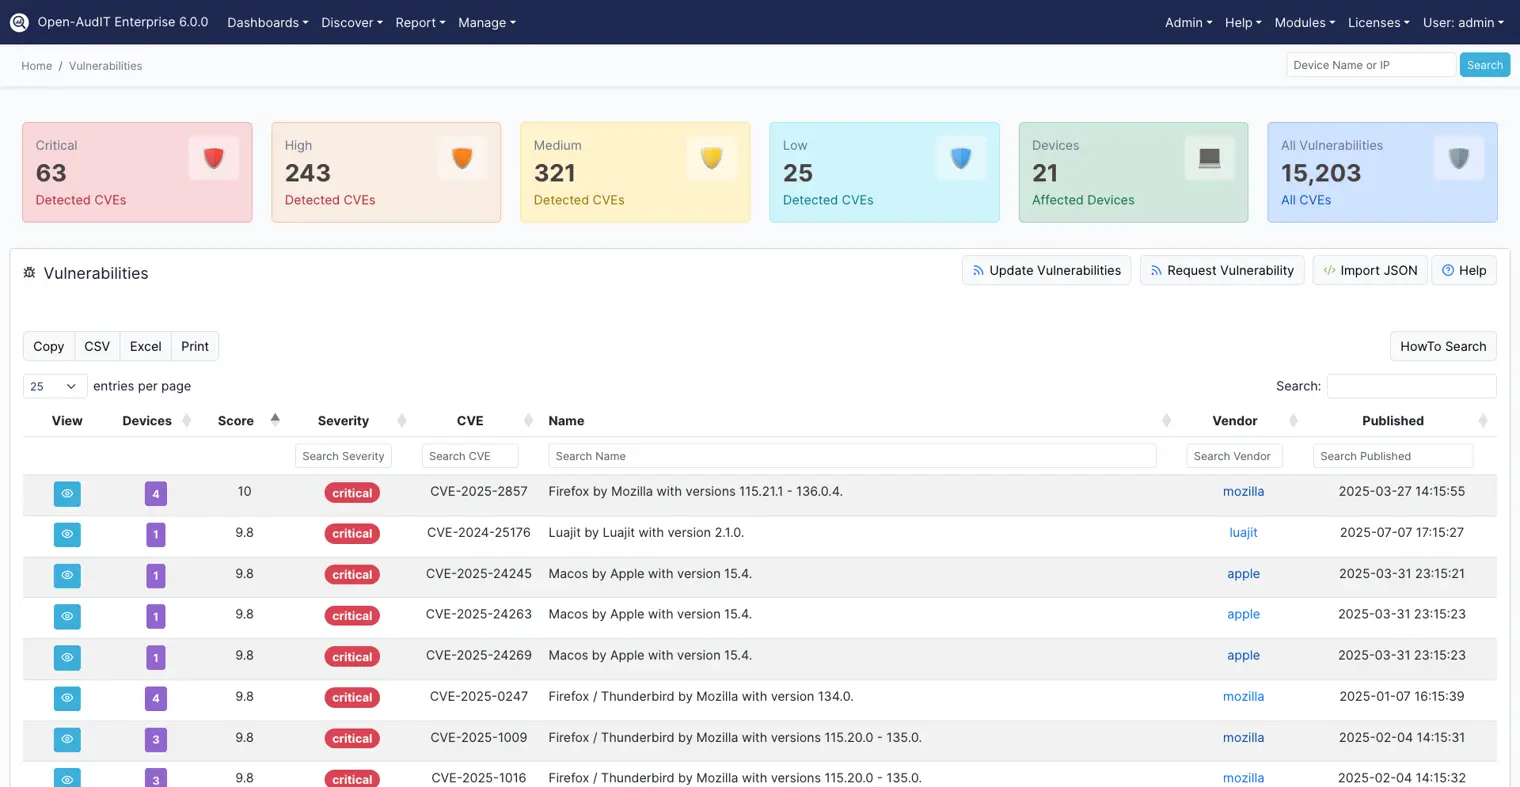
Cross-reference discovered software and firmware against the NVD to surface CVEs relevant to your environment.
Open-AudIT cross-references your discovered software and firmware versions against the NIST National Vulnerability Database, so you only see CVEs that actually apply to your environment. AI matches CVEs to the devices you have discovered and alerts you.
Compliance Reporting. (Enterprise) (commercial edition)
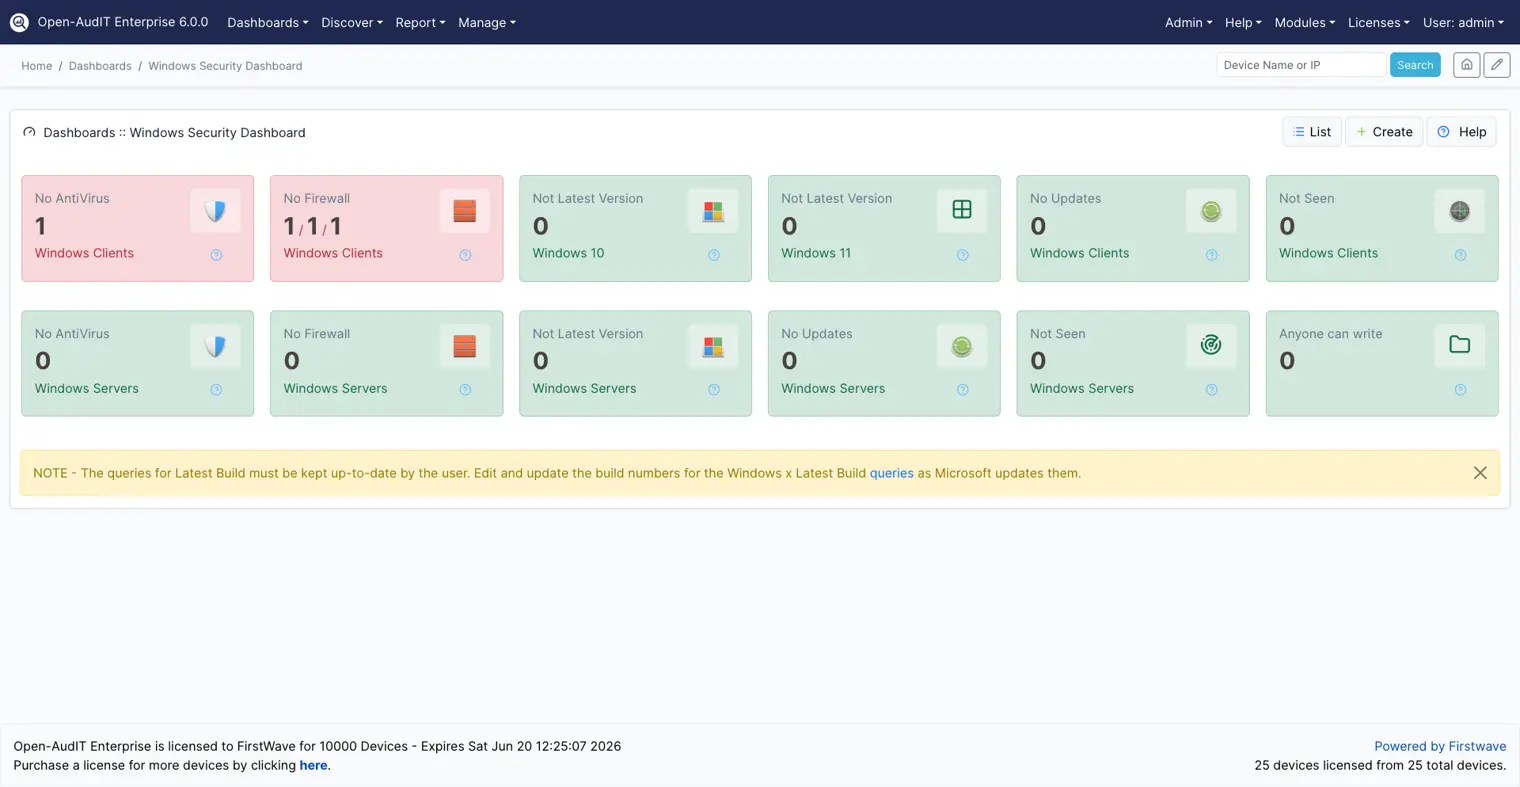
Check your network against the DISA STIGs and CIS Benchmarks, and report against ISO 27001, CBDDO, BDDK, NCA ECC and ASD Essentials, with automated audit reports.
Ship-with reports cover software licensing, changes and security posture. Check your network against the DISA STIGs and CIS Benchmarks, and report against ISO 27001, CBDDO, BDDK, NCA ECC and ASD Essentials controls, with automated audit evidence.
Multi-site & MSP Ready. (Enterprise) (commercial edition)
Deploy collectors across distributed networks and consolidate results into a single inventory.
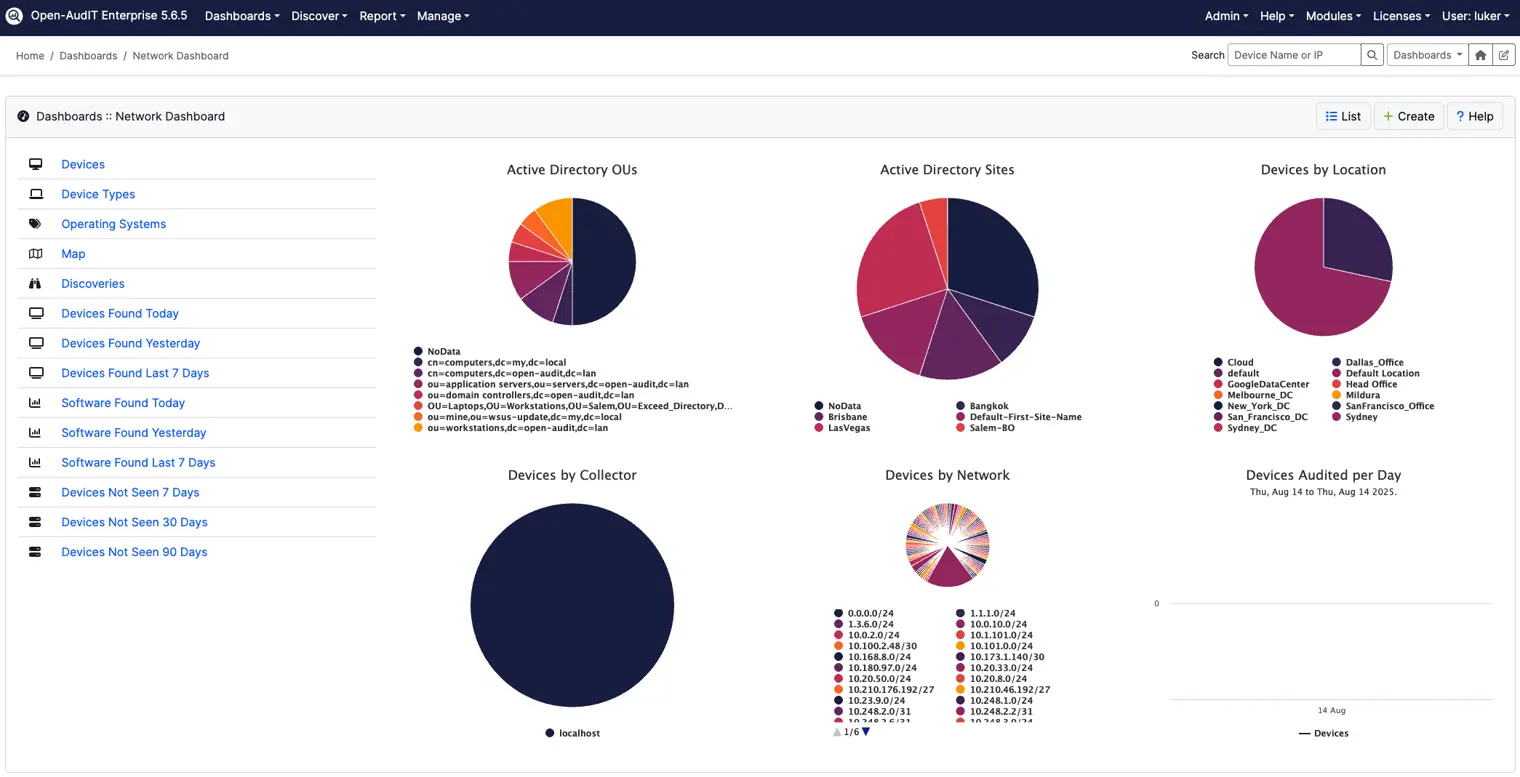
Collectors run discovery in remote networks and report back to a central server, consolidating distributed sites (or entire client fleets, for MSPs) into one inventory.
What Open-AudIT collects
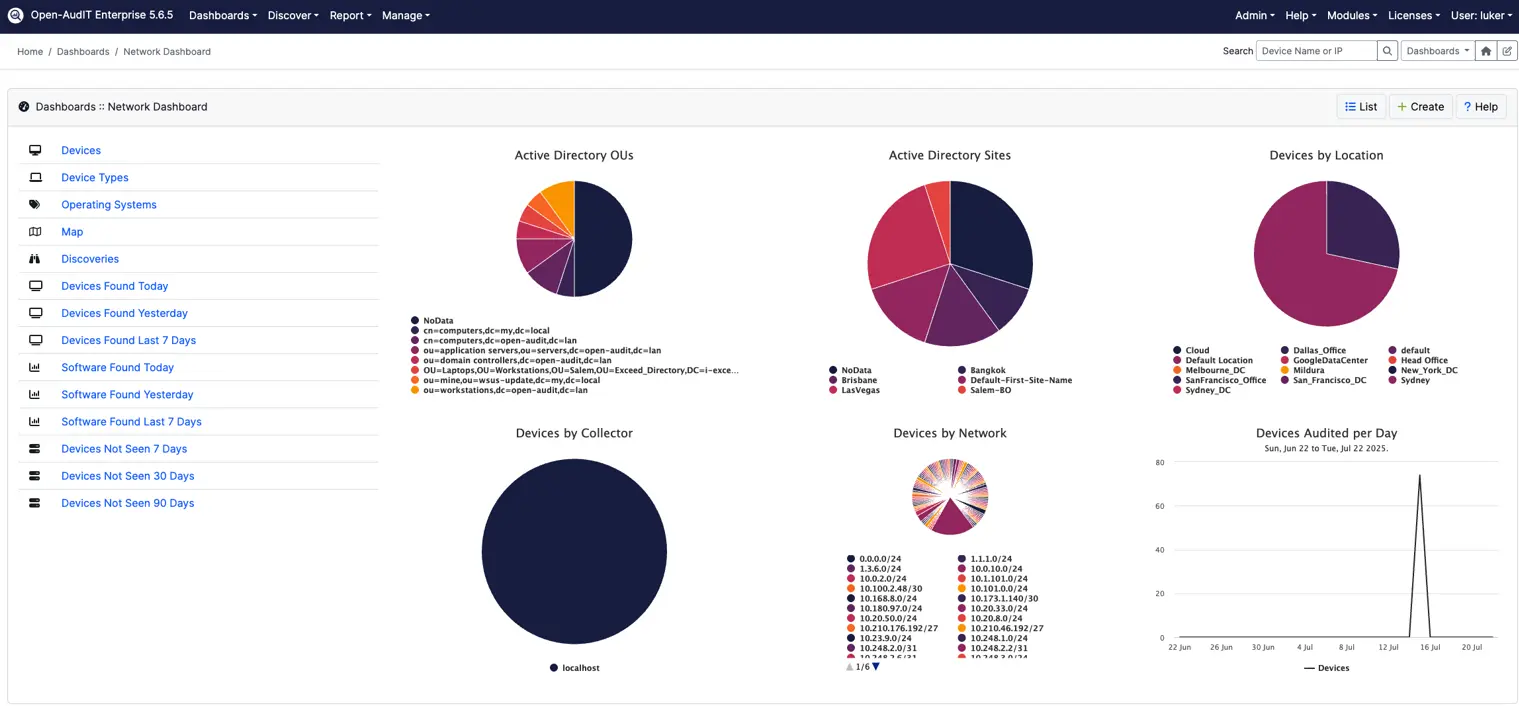
Each audited device contributes hundreds of attributes to your inventory. A sample of what is captured:
Hardware
- Motherboard, CPU and memory
- Hard disks and partitions
- Network cards and MAC addresses
- Monitors and attached peripherals
- Serial numbers and asset tags
- Virtual machine host and guest details
Software
- Installed applications and versions
- Running services and daemons
- Users and groups
- Network shares
- Databases and web sites on servers
OS & settings
- Operating system name and version
- Installed patches and updates
- IP configuration and routes
- Scheduled tasks
- Security and firewall settings
- Warranty and purchase data via custom fields